Customer Portal Talk to an expert
Cybersecurity Journey · NIST CSF 2.0

Detect and Respond: from the first signal to restored operations

The third phase of the Journey brings together three NIST CSF 2.0 functions: Detect, Respond and Recover. The Cyber Defense Center, the Vortex Converged NG-SOC (NG-SOC Convergente), monitors IT and OT 24x7x365 and responds to incidents, and continuity planning prepares recovery.

In short: The Detect and Respond phase of the Vortex Cybersecurity Journey covers three NIST CSF 2.0 functions: Detect, whose outcome is “Possible cybersecurity attacks and compromises are found and analyzed”; Respond, whose outcome is “Actions regarding a detected cybersecurity incident are taken”; and Recover, whose outcome is “Assets and operations affected by a cybersecurity incident are restored.” It combines technologies such as NDR, Threat Intelligence (CTI), XDR and OT-Threat Detection with the 24x7x365 SOC and MDR of the Cyber Defense Center, the Vortex NG-SOC Convergente, which brings together continuous monitoring, threat intelligence, automation and specialists, from initial triage to response. The incident response and digital forensics (DFIR) retainer contains, investigates and eradicates attacks, and business continuity and disaster recovery (BCDR) planning prepares recovery, with business impact analysis, recovery strategies and testing.

NIST CSF 2.0

What Detect, Respond and Recover ask for, and how Vortex delivers it

In NIST CSF 2.0, the Detect function has two categories, Respond has four and Recover has two. In the Vortex Journey, the three are in a single phase: detection feeds response, and response ends in recovery.

CategoryWhat the framework asks forHow Vortex delivers it
Continuous Monitoring (DE.CM)Networks, the physical environment, personnel activity and technology usage, external service provider services, and computing hardware, software and data monitored to find potentially adverse events (DE.CM-01 to DE.CM-09)24x7x365 monitoring by the Cyber Defense Center, with SIEM-as-a-Service; network traffic analyzed by NDR; endpoint, network, identity, cloud and email telemetry correlated in XDR; identity threats in AD and Entra ID (ITDR); decoys against attackers already inside the perimeter (Deception); in OT, industrial protocols monitored in real time. Monitoring of the physical environment (DE.CM-02) is not part of the catalog
Adverse Event Analysis (DE.AE)Events analyzed to understand what is happening; information correlated from multiple sources; impact and scope estimated; threat intelligence integrated into the analysis; incident declared when the criteria are met (DE.AE-02 to DE.AE-08)AI triage, which classifies alerts and filters out false positives before the analyst; correlation of data from multiple sources; enrichment in more than 150 external sources; threat intelligence (CTI), including from the deep and dark web; Tier 1 to 3 analysts
Incident Management (RS.MA)Incident response plan executed in coordination with relevant third parties once an incident is declared; incidents triaged, categorized, prioritized and escalated as needed; criteria for initiating recovery (RS.MA-01 to RS.MA-05)Cyber Defense Center service from initial triage to technical and strategic response, with a reference SLA of 15 minutes for the first response to high-severity incidents; playbooks that automate triage, enrichment and containment (SOAR). The response plan belongs to the company; the tabletop exercises that test it are in the Identify phase
Incident Analysis (RS.AN)Analysis of what has taken place and of the root cause; actions recorded; incident data and metadata collected, with their integrity and provenance preserved; magnitude estimated and validated (RS.AN-03 and RS.AN-06 to RS.AN-08)Investigation and digital forensics through the incident response retainer (DFIR); AI copilot that summarizes IoCs, correlates threat intelligence and suggests hypotheses
Incident Response Reporting and Communication (RS.CO)Internal and external stakeholders notified of incidents; information shared with designated stakeholders, according to the response plan (RS.CO-02 and RS.CO-03)War room with IT and, in OT, with the plant; remediation tracked in the portal. Notifying regulators, customers and data subjects, such as notifying the ANPD (Brazil’s data protection authority) under Brazil’s LGPD (General Data Protection Law), is up to the company, with the facts established by the investigation
Incident Mitigation (RS.MI)Incidents contained and eradicated (RS.MI-01 and RS.MI-02)Automated containment by playbooks, such as machine quarantine and IP blocking; response orchestrated by XDR; containment and eradication by DFIR. EDR, deployed in the Protect phase, also contains attacks on the endpoint
Incident Recovery Plan Execution (RC.RP)Recovery plan executed once initiated by the response; actions prioritized; integrity of backups verified before restoring; normal operating status confirmed; end of recovery declared and documented (RC.RP-01 to RC.RP-06)Business continuity and disaster recovery (BCDR) planning, with business impact analysis (BIA), recovery strategies and testing. Backup and restore are not part of the catalog
Incident Recovery Communication (RC.CO)Recovery activities and progress communicated to designated stakeholders; public updates shared using approved methods and messaging (RC.CO-03 and RC.CO-04)Not part of the catalog: it stays with the company, through the crisis communication plan

Categories and subcategories summarized by Vortex from NIST CSWP 29, The NIST Cybersecurity Framework (CSF) 2.0, February 26, 2024 (official text).

How Vortex does it

From signal to recovery

The Cyber Defense Center works the incident from the first signal to closure, and what is learned goes back to the Identify phase.

  1. Detect

    What is happening in the environment?

    What you get

    • 24x7x365 monitoring of IT and OT on the same platform
    • Network, endpoint, identity, cloud and email telemetry correlated
    • Decoys that reveal the attacker already inside the perimeter
  2. Analyze

    Is it an incident, and how big is it?

    What you get

    • AI triage, which filters out false positives before the analyst
    • Enrichment in more than 150 external sources and threat intelligence
    • Specialists where business context decides
  3. Respond

    How do you contain the attack?

    What you get

    • Playbooks that automate containment, such as quarantine and IP blocking
    • War room with IT and, in OT, with the plant
    • Investigation, containment and eradication by DFIR
  4. Recover

    How do you get back to normal, and what changes afterward?

    What you get

    • Continuity and recovery plan prepared with BCDR
    • Remediation tracked in the portal
    • Playbooks reviewed and improvements taken to the Identify phase (ID.IM)

The inventory and the priorities come from the Identify phase, and the safeguards of the Protect phase generate the logs and telemetry that the Cyber Defense Center monitors.

Technologies and services in the Detect and Respond phase

Grouped by the three NIST CSF 2.0 functions the phase covers. EDR and OT-EDR, deployed in the Protect phase, also feed detection and containment.

Detect (DE) 7

Detect (DE)

Network Detection and Response (NDR)

Network Detection and Response is a technology that monitors network traffic in real time, detecting anomalous patterns and potential threats based on behavioral intelligence and flow analysis. The tool collects network data, applies machine learning and correlates information to identify suspicious activity, offering advanced visibility and enabling rapid response to incidents in progress.

1 of 11

Respond (RS) 3

Recover (RC) 1

  1. The foundation With these technologies, we establish a solid foundation for proactive detection and effective response to cyber incidents.
  2. More than tools But detecting and reacting quickly to threats takes more than good tools — it requires a coordinated, continuous and specialized operation.
  3. Cyber Defense Center That is why, beyond these technologies, we work through our Cyber Defense Center, the Vortex NG-SOC Convergente, which brings together intelligence, automation and expertise in a managed service.

Cyber Defense Center: our incident detection and response service

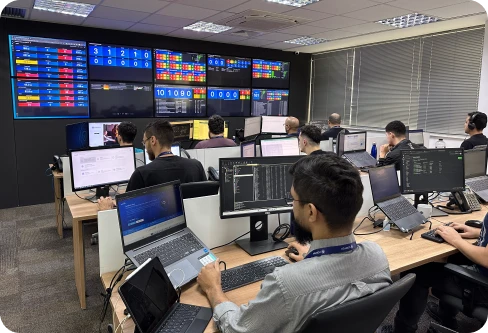
Analysts monitoring threats in a security operations center
  • The service The Cyber Defense Center (CDC) is our managed cyber incident detection and response service, designed to protect IT and OT environments in an integrated, continuous and intelligent way. Based on an NG-SOC Convergente model, we bring together 24x7x365 monitoring, threat intelligence, process automation and the expertise of cybersecurity specialists to detect, analyze and respond to events with speed and precision.
  • From signal to response Our NG-SOC Convergente correlates data from multiple sources, identifies suspicious behavior and turns signals into actionable alerts. We act from initial triage to technical and strategic response, with visibility, rapid mitigation and support throughout the incident life cycle.
  • The result More than monitoring, we deliver coordinated action and informed decision-making, raising your organization’s cyber maturity.
Go deeper

Service and guides

Cyber Defense Center

The Vortex NG-SOC Convergente: 24x7x365 detection and response for IT, OT and AI, with hyperautomation and specialists.

Discover the CDC

Guide: incident response plan

Roles, communication, playbooks, evidence and recovery, the NIST phases, the ransomware case and notification to the ANPD.

Read the guide (PT)

Guide: SIEM, SOAR, EDR, XDR and NDR

What each one sees and does, the difference in a table and how they come together in the SOC, from collection to response.

Read the guide (PT)

Frequently asked questions

Which NIST CSF 2.0 functions does the Detect and Respond phase cover?

Three of the six: Detect (DE), whose outcome is “Possible cybersecurity attacks and compromises are found and analyzed”; Respond (RS), whose outcome is “Actions regarding a detected cybersecurity incident are taken”; and Recover (RC), whose outcome is “Assets and operations affected by a cybersecurity incident are restored.” Detect has two categories, Continuous Monitoring (DE.CM) and Adverse Event Analysis (DE.AE); Respond has four, Incident Management (RS.MA), Incident Analysis (RS.AN), Incident Response Reporting and Communication (RS.CO) and Incident Mitigation (RS.MI); Recover has two, Incident Recovery Plan Execution (RC.RP) and Incident Recovery Communication (RC.CO) (NIST CSF 2.0).

What is ransomware and how does the SOC respond?

Ransomware is malware that encrypts an organization’s files and systems and demands payment to restore access; attackers often also steal the data and threaten to sell or publish it if the ransom is not paid (NIST IR 8374; CISA). The SOC looks for the signs of compromise that precede the impact, such as suspicious behavior and lateral movement, and coordinates the response, with playbooks that automate triage, enrichment and containment. At Vortex, the Cyber Defense Center, the NG-SOC Convergente, acts from initial triage to response; the incident response and digital forensics (DFIR) retainer contains, investigates and eradicates the attack; and business continuity and disaster recovery (BCDR) planning prepares recovery.

What is SIEM?

SIEM (Security Information and Event Management) is the platform that centralizes the logs and security events of the entire environment, such as firewalls, servers, identities, cloud and applications, correlates those events and generates alerts; it also stores the logs for investigation and auditing (NIST). Without a SOC, the SIEM generates alerts that nobody investigates. In the Vortex SIEM-as-a-Service, the platform is hosted and fully operated by Vortex, and the company consumes the service by sending its logs.

What is the difference between SIEM, SOAR, EDR, XDR and NDR?

Each one covers a part of detection and response. SIEM centralizes and correlates the logs of the entire environment and generates the alerts. SOAR runs playbooks that automate triage, enrichment, containment and response. EDR detects and responds on workstations and servers. NDR analyzes network traffic and finds lateral movement, command and control and exfiltration, including on equipment that cannot take an agent. XDR correlates endpoint, network, identity, cloud and email in a single platform. None of them replaces the operation that investigates and decides: the SOC. The guide to SIEM, SOAR, EDR, XDR and NDR (PT) compares the five in a table.

What is threat intelligence (CTI)?

It is information about cyber threats that has been aggregated, analyzed and enriched to provide context for decisions (NIST SP 800-61r3): indicators of compromise, attacker tactics and techniques and monitoring of the deep and dark web for leaked credentials, data leaks and phishing campaigns against the company. In NIST CSF 2.0, threat intelligence is part of event analysis (DE.AE-07). At Vortex, it enriches the alerts of the Cyber Defense Center and guides detection.

What is threat hunting?

It is the proactive search, carried out by analysts, for signs of attack that rules and use cases do not yet detect, over the telemetry already collected. It goes hand in hand with detection engineering, which creates and tunes rules based on what is learned. In the Cyber Defense Center, proactive threat hunting on the collected telemetry and continuous detection engineering, aligned with MITRE ATT&CK, are part of the service.

What is lateral movement and how is it detected?

It is the tactic in which the attacker, already inside the environment, moves from one system or account to others until reaching the target, often with legitimate credentials and native tools, which makes it stealthy (MITRE ATT&CK, TA0008). In the Detect and Respond phase, three technologies help to see it: NDR, which analyzes network traffic; deception technology, with honeypots and honeytokens in which any interaction is suspicious; and ITDR, which detects compromised accounts, privilege escalation and lateral movement via identity in AD and Entra ID.

What should an incident response plan include?

The plan defines, before an attack, how the company detects, contains, eradicates and recovers from an incident: who leads and decides, how the incident is classified, who is notified and when, which playbooks to follow, how to preserve evidence and how to restore systems (NIST). For NIST, it needs to be maintained, tested and synchronized with the business continuity plan (NIST SP 800-61r3). The incident response plan guide (PT) details each part, with the ransomware case and notification to the ANPD, Brazil’s data protection authority.

What is the difference between an incident response plan and a business continuity plan?

The incident response plan puts the company’s response capability into practice: roles, classification, communication, playbooks, evidence, recovery and lessons learned. The business continuity and disaster recovery plan reduces disruption to operations in serious situations, not only attacks, based on business impact analysis (BIA) and risk assessment. The two need to work together. At Vortex, business continuity and disaster recovery (BCDR) planning includes the BIA, recovery strategies and testing.

What is DFIR?

DFIR (Digital Forensics and Incident Response) is the combination of incident response, which contains, investigates and eradicates the attack, with digital forensics, which preserves and analyzes the evidence to reconstruct what happened. In the Vortex incident response retainer, the response and forensics team is available under contract before the incident happens, to contain, investigate and eradicate attacks quickly.

Does the Detect and Respond phase include recovery?

It includes the planning. BCDR prepares business continuity and disaster recovery, with business impact analysis (BIA), recovery strategies and testing. Backup and restore are not part of the Vortex catalog. In NIST CSF 2.0, recovery begins when the response process initiates it and ends when normal operating status is confirmed and the end of recovery is declared and documented (RC.RP-01, RC.RP-05 and RC.RP-06).

Who notifies the ANPD, Brazil’s data protection authority, of the incident?

The company, as the data controller. When the incident affects personal data and may cause relevant risk or harm to the data subjects, Brazil’s LGPD (General Data Protection Law) requires notifying the ANPD and the data subjects within three business days, under Resolução CD/ANPD nº 15/2024. The DFIR investigation and digital forensics help establish what happened and what was affected. The incident response plan guide (PT) shows the flow.

How does detection and response work in OT?

OT-Threat Detection monitors industrial protocols, networks and devices in real time and detects atypical behavior and signs of attack. In the Cyber Defense Center, IT and OT are monitored on the same platform, and correlation shows when an attack that started in the office reaches the plant; the response is coordinated in a war room with IT and with the plant team.

Talk about detection and response

Tell us a little about your environment and how incidents are handled today. A Vortex specialist will get back to you to talk about the Cyber Defense Center.

  • 24x7x365 detection and response in IT and OT
  • Reference SLA of 15 minutes for the first response to high-severity incidents
  • Service by Vortex specialists

By submitting, you confirm that you have read the Privacy Policy (PT). Vortex uses this data to reply to your request.

Updated on